Use role-based access control with conservative defaults: give most users read-only access, grant edit rights only where a task requires them, avoid broad delete permissions, and maintain at least two admin accounts. This structure, drawn from the NIST RBAC model, keeps collaborative art inventories accurate and prevents a single mistake or departure from compromising the collection record.
TL;DR:
- Assign most users read-only permissions and restrict delete rights to administrators to prevent accidental loss of records.
- Use role-based access control with multiple administrative accounts and session activation to reduce the risk of lockouts and limit exposure.
- Apply permissions at folder levels based on actual workflows, and create overrides only for exceptional cases that are reviewed periodically.
- Separate roles so no single person controls an entire transaction, ensuring checks and accountability in cataloging, valuation, and sales workflows.
- Regularly review access rights, maintain detailed audit logs, and document overrides to avoid permission drift and ensure security over time.
Table of Contents
- Understanding role-based access control for art inventories
- How granular should your permission levels be?
- Where to apply permissions in your folder structure
- Mapping roles to cataloging, valuation, sales, and loan workflows
- Keeping permissions accurate: audits, reviews, and admin redundancy
- Avoiding the most common permission mistakes
- How Artworksoft handles user permissions and access control
- Getting the priorities right for a small team
- Put this permission model to work with Artworksoft
- Sources
- FAQ
Understanding role-based access control for art inventories
Role-based access control assigns permissions to roles, not to individual people. A gallery registrar, a valuation manager, and a guest reviewer each get a role, and that role carries a defined set of permissions across the collection. When staff change, administrators reassign the role rather than rebuilding access from scratch.
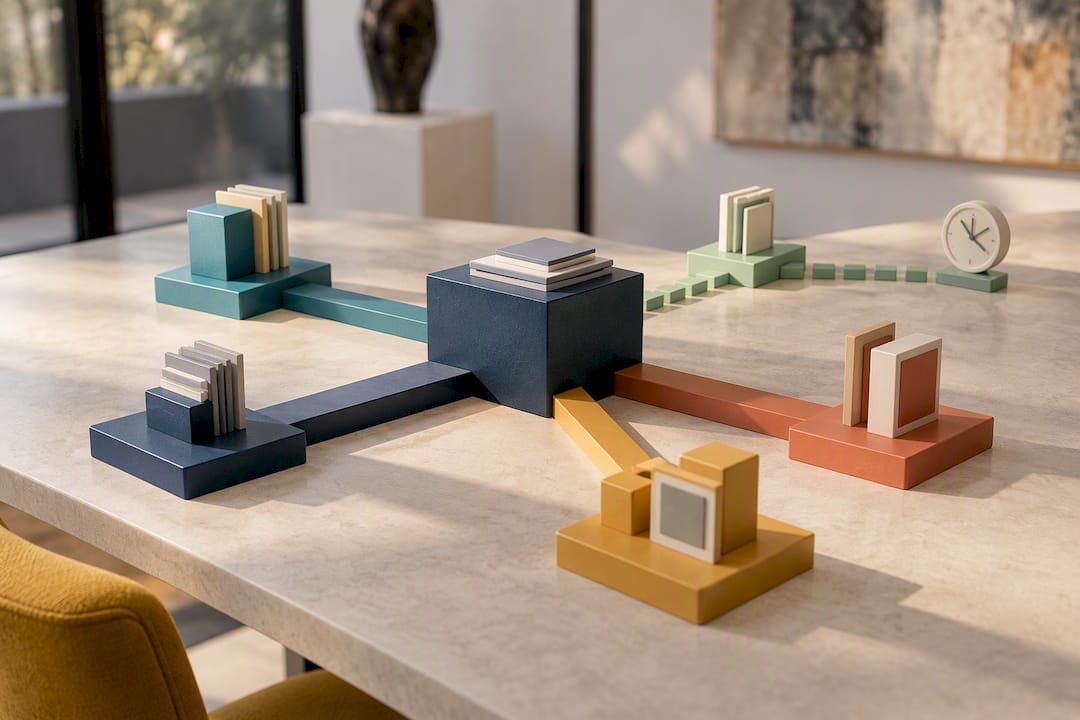
The NIST RBAC reference model describes this system through five components: users, roles, permissions, operations, and objects. A permission is really a pairing of an operation (view, edit, delete) with an object (an artwork record, a folder, a valuation field). Roles bundle permissions together so administrators manage a handful of roles instead of hundreds of individual settings.
Two relationships matter most in practice:
- User-role mapping is many-to-many. One person can hold multiple roles, such as cataloger and sales assistant, and one role can apply to many people.
- Role-permission mapping is also many-to-many. A single permission, like editing provenance notes, might belong to both a registrar role and a curator role.
Most systems also support session activation, meaning a user with several roles can activate one or more of them for a given session rather than carrying every permission at once. A registrar who also handles occasional sales might work most days under a cataloging role and switch to a sales role only when processing a transaction. This narrows the exposure window and makes activity logs easier to interpret. The NIST administrative functional specification treats this kind of role review and activation control as a core part of RBAC, not an optional extra, because it directly reduces the chance of accidental or fraudulent changes.
How granular should your permission levels be?
Most art inventory platforms split permissions into four tiers, a structure generally documented across inventory management systems: view, add, change, and delete. Each tier should map to a specific need rather than a job title.
- View lets a user see records without altering anything, suitable for guests, appraisers, or insurance contacts.
- Add allows new records to be created, useful for interns or cataloging assistants entering new acquisitions.
- Change permits edits to existing fields such as location, condition notes, or exhibition history.
- Delete removes records entirely and should be the most restricted tier in any collection.
Beyond these tiers, many collections benefit from attribute-level splits. A cataloger might need to edit location and photo fields but never touch price or provenance. A valuation manager might need the opposite: full access to pricing history and appraisal notes, with no ability to change movement records. Splitting permissions this finely protects the fields most likely to cause disputes or compliance issues if altered without approval.
Because delete operations are irreversible in most systems, inventory documentation recommends limiting who holds that permission and, where the platform allows it, using an archive or soft-delete workflow instead. An archived record stays retrievable if the removal turns out to be a mistake, while a hard delete does not.
Pro Tip: Reserve delete permissions for one or two administrators, and default every new contributor role to add and change only.
Where to apply permissions in your folder structure
Applying permissions at the folder or collection level, rather than to each artwork individually, lets new items inherit the correct access automatically. This is the approach described in access control documentation for hierarchical systems: set the rule once at the parent level and every item placed inside follows it.
A practical setup often looks like this:
- Create top-level folders by function. Common divisions include permanent collection, active exhibition, storage, and loans out.
- Set base permissions at each folder. Storage might be view and add for most staff, while loans out might require change access only for the registrar role.
- Apply overrides only where a single item needs different treatment. A newly acquired piece under appraisal might need a temporary override restricting price visibility, even though the rest of the storage folder is open for viewing.
- Review overrides periodically. Exceptions that outlive their reason tend to accumulate quietly and complicate future audits.
Folder schemes built around real workflows, such as gallery floor, offsite storage, exhibition loan, and consignment, tend to hold up better over time than schemes built around departments alone, since artwork moves between physical states more often than staff change roles. Overrides should stay the exception, not the default: a scheme with a handful of clean folder-level rules and a small number of documented exceptions is far easier to audit than one where every item carries its own custom settings.
Mapping roles to cataloging, valuation, sales, and loan workflows
A useful role map starts with the actual work being done, not with job titles that vary between organizations. Six templates cover most collaborative art inventories:
- Guest or viewer: read-only access to selected folders, often used for insurance agents, appraisers, or prospective buyers.
- Cataloger or contributor: add and change permissions on descriptive fields, no access to pricing or delete.
- Registrar or curator: change permissions across location, condition, exhibition, and provenance fields, with add access for new records.
- Valuation manager: change access to pricing and appraisal fields, often paired with view-only access elsewhere.
- Sales or transactions: change access limited to transaction records and buyer information, separate from cataloging fields.
- Admin: full access, including delete and user management, held by no more than two or three people.
Separation of duties keeps any single role from controlling an entire transaction end to end. A cataloger who creates a record should not be the same person who approves its final sale price, and a registrar tracking a loan should not be the one authorizing the valuation change tied to insurance coverage. This split mirrors the administrative intent behind role review practices in the NIST model: permissions should follow the task, and a second set of eyes on high-stakes changes catches errors before they become part of the permanent record.
Security practitioners writing about practical RBAC deployment recommend starting with standard default roles that cover common workflows and adding custom overrides only when a specific task demands it. Overrides that accumulate unchecked create permission sprawl, where nobody remembers why a particular user has a particular exception.
Pro Tip: Write a one-line rationale next to every custom override at the time you create it. Six months later, that note is the only thing that tells you whether the exception still makes sense.
Keeping permissions accurate: audits, reviews, and admin redundancy
Permissions drift over time as staff join, leave, or change responsibilities. A short operational routine keeps the role map honest:
- Review roles and access quarterly, or immediately after any staff change. A departing employee’s access should be revoked the same day, not at the next convenient review.
- Keep audit logs and exportable access reports. A record of who changed what, and when, matters for insurance claims, provenance disputes, and internal accountability alike. The NIST administrative specification lists logging and role-change history among the core administrative functions that make RBAC auditable rather than just theoretical. Regular collection audits that include a permission check alongside a physical inventory check catch both types of discrepancy at once.
- Maintain multiple trusted admin accounts to avoid lockout and provide continuity. Practitioners writing about disaster recovery and account continuity planning recommend this as standard practice: a single admin who leaves, loses credentials, or becomes unreachable should never be able to lock an organization out of its own records.
- Document a recovery process before it is needed. Write down who can reset admin access, where recovery credentials are stored, and how a second admin verifies the request.
Treat delete permissions and admin-level flags as actions requiring documented approval, reconfirmed at every review cycle rather than assumed to still be appropriate. A role that made sense a year ago, when the organization had three staff members, may be far too broad once that number doubles.
Avoiding the most common permission mistakes
Three mistakes account for most of the trouble collaborative teams run into.
- Over-permissive delete access. Granting delete to anyone who asks for convenience is the single most common way a collection loses records it cannot recover.
- Permission sprawl. Custom overrides added ad hoc, without documentation, eventually make it impossible to tell why any given user has any given access.
- Single-admin lockout. One administrator, one point of failure. A departure, a lost password, or a forgotten multifactor device can freeze an entire organization out of its own inventory.
When something looks wrong, three checks usually find it fast: test the affected permission with a sandbox or guest user rather than a live account, check whether the issue traces back to folder-level inheritance rather than an individual setting, and review the role-change log to see what changed and when.
For small teams, two collaboration patterns work well: branch or department roles that mirror how the organization is actually structured, and temporary guest links with automatic expiration for external reviewers such as appraisers or press contacts who need short-term access without a permanent account.
How Artworksoft handles user permissions and access control
Artworksoft applies the same role-based structure described throughout this guide directly to art collection workflows. Roles align to the tasks collections actually involve: cataloging, valuation, sales, loans, and movement tracking, so a contributor entering new pieces and a valuation manager reviewing pricing history work within the scope their job requires.
The platform supports the practical controls this guide recommends:
- Granular permission toggles that separate view, add, change, and delete rights by field and folder rather than applying one blanket setting.
- Support for multiple admin accounts, so no single login holds sole control over the collection.
- Shareable read-only links for guests, appraisers, or buyers who need to view artwork profiles without editing them.
- Exportable audit reports that support the review cadence described above, alongside documentation tools for generating Certificates of Authenticity and provenance records tied to specific roles.
New Artworksoft users setting up a collaborative team benefit from starting with view-only defaults for most contributors, adding add and change permissions only where a workflow requires them, and requesting the onboarding service for larger or institutional collections that need a role map built around existing staff structures from day one.
Getting the priorities right for a small team
Most small galleries and independent artists overthink the permission model before they set it up and underthink it once it is running. Start simple: two admins, everyone else on read-only or narrowly scoped edit access, and a short written note explaining why each exception exists. That note matters more than any software setting, because it is what lets a future administrator understand a decision made months earlier without guessing.
The real trade-off is convenience against auditability, and it shifts with the value of the collection. A handful of low-value student works tolerates loose permissions. A collection with six-figure pieces does not, and every added contributor should come with a corresponding review of what they can touch. Institutional collections, or any group managing work across multiple staff and locations, tend to benefit from a paid onboarding service that maps roles to the organization’s actual structure rather than a generic template.
— Nealda
Put this permission model to work with Artworksoft
Artworksoft is built to support the role structure this guide describes: granular permission toggles, multiple admin accounts, shareable read-only links, and audit-ready reports that keep a collaborative team accountable without slowing anyone down. Setting these controls up correctly from the start costs far less time than untangling permission sprawl a year later.
The Free Plan lets a small team test role assignments and folder permissions directly, and the Provenance Plan adds the branded documentation and analytics that larger collections tend to need, starting at $5 per month. Organizations managing institutional or multi-location collections can request the onboarding and collection management service to have a role map built around their existing staff before launch. Visit Artworksoft to get started.
Sources
- Role Based Access Control | CSRC
- InvenTree — User permissions documentation
- Copyright Office circular: Fair Use (and related guidance)
FAQ
Why do artists not allow reposts of their work?
Artists control reposting to protect their exclusive rights under copyright law, since the U.S. Copyright Office confirms that owners retain the right to decide how and where their work is reproduced. Unauthorized reposting can also strip attribution and context that the artist considers part of the work’s presentation.
What is the 70/30 rule in art?
There is no single, universally recognized “70/30 rule” defined by a copyright authority or standards body. The phrase is used informally in different contexts, such as gallery commission splits or composition guidelines, so its meaning depends on who is using it and should be confirmed with the specific source.
Can someone use your art without permission?
Generally, no. The U.S. Copyright Office advises that written authorization is recommended whenever reuse is uncertain, since fair use is a case-by-case legal determination made by courts, not a status the Copyright Office grants in advance.
What is the best app for managing an art inventory?
The right tool depends on collection size, budget, and whether the team needs collaborative permissions. Artworksoft offers a Free Plan alongside role-based access controls, valuation tools, and documentation features designed for artists, collectors, and galleries managing collaborative inventories.
How do I choose the right permission level for a new team member?
Start with read-only access and add specific permissions, like adding new records or editing certain fields, only as their role requires them. This least-privilege approach, consistent with the NIST RBAC model, limits accidental changes while still letting each person do their job.